
Regulatory compliance
Regulatory compliance from obligation to operation
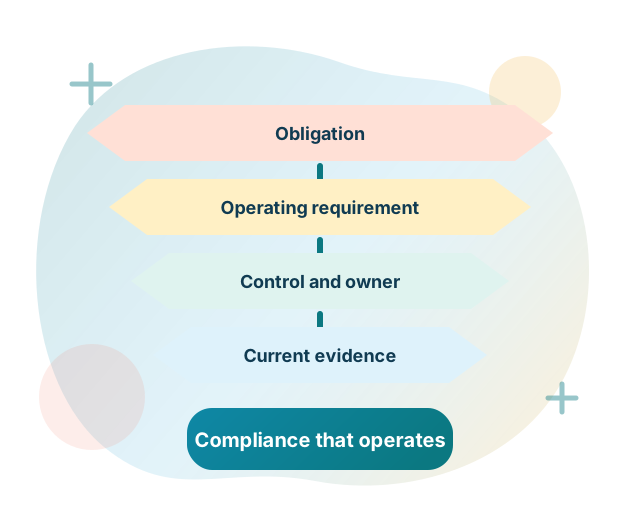
Connect each material obligation to an owner, control, evidence, monitoring and change instead of managing compliance as a separate document exercise.
What does the obligation change in day-to-day work?
A requirement is difficult to manage when it sits in one document, the related policy sits somewhere else and evidence of the control is collected only when an audit begins.
We help connect what is required to the person responsible, the control that addresses it, the evidence that shows whether the control is working and the action taken when it is not.
From obligation to operation
For example, an obligation to restrict access to sensitive information may connect to an access policy, approval process, system configuration, periodic review, exception record and evidence retained for assurance. If one of those parts changes, the organisation should be able to see what else is affected.
An engagement can cover:
- the obligations and policy commitments within the agreed scope
- control design, ownership and responsibility
- evidence and assurance activity
- monitoring, exceptions and management reporting
- remediation across policy, process, people, information and technology
Experience in financial services
For one large financial institution, Hot Desk assessed the current environment, designed an IRM and compliance programme and target architecture, developed a roadmap and supported stakeholder alignment. The work continued through deployment of Parapet in the customer's cloud environment and integration with critical enterprise systems.
Parapet formed part of this delivered work, so the example shows our programme and implementation experience rather than an independent software-selection process. We do not attach outcomes that the available evidence does not support.
Technology may be only part of the answer
We can define the requirement and assess process, control and technology options before a product decision. The recommendation may be better use of an existing platform, another product, Parapet or no platform change.
Our role is to help the organisation make and implement a practical decision. We do not provide legal advice or promise regulatory acceptance, certification or a particular compliance outcome.
Discuss your compliance challenge, or explore related IRM, security and government advisory.
Start a conversation
Bring us the challenge, not a finished specification.
We will help clarify the current state, the decisions that matter and a practical next step.